Browse our range of reports and publications including performance and financial statement audit reports, assurance review reports, information reports and annual reports.
Request for audit
Responded: Friday 17 December 2021
Response provided
The Auditor-General responded on 17 June 2021 to correspondence from the Hon Mark Dreyfus QC, MP dated 21 May 2021, requesting that the Auditor-General conduct an investigation to examine how part-time members of the Social Services and Child Support Division and “sessional part-time members” in the Migration and Refugee Division of the Administrative Appeals Tribunal are being remunerated.
The Auditor-General provided a follow-up response to the Hon Mark Dreyfus QC, MP on 17 December 2021.
Contact
Please direct enquiries relating to requests for audit through our contact page.
About
Updated: Friday 23 May 2025
Updated
The ANAO’s governance structure and practices support the Auditor-General in the oversight of the organisation, management of its resources and the delivery of quality audit products. The corporate governance framework, processes and related organisational capability supports the delivery of the ANAO’s purpose, and meets public and community expectations of probity, accountability and transparency.
Contact
Please direct enquiries through our contact page.
Request for audit
Responded: Thursday 12 April 2018
Response provided
The Auditor-General responded on 23 November 2017 to correspondence from Senators Abetz, Paterson and Reynolds dated 27 October 2017, requesting that the Auditor-General undertake an examination of the administration and governance arrangements relating to the Student Services and Amenities Fee (SSAF). Following a request from Senator Abetz on 17 January 2018 for a more detailed response, the Auditor-General followed-up on 5 April 2018.
Contact
Please direct enquiries relating to requests for audit through our contact page.
Insights: Audit practice
Published: Wednesday 6 November 2024
Published
This edition is intended for officials within government entities responsible for governance, internal audit or a government activity that may be the subject of an ANAO performance audit. The purpose of Insights: Audit Practice is to explain ANAO methodologies to help entities prepare for an ANAO audit.
Contact
Please direct enquiries through our contact page.
Other report (Auditor-General Report No. 27 of 2019–20)
Published: Wednesday 11 March 2020
Published
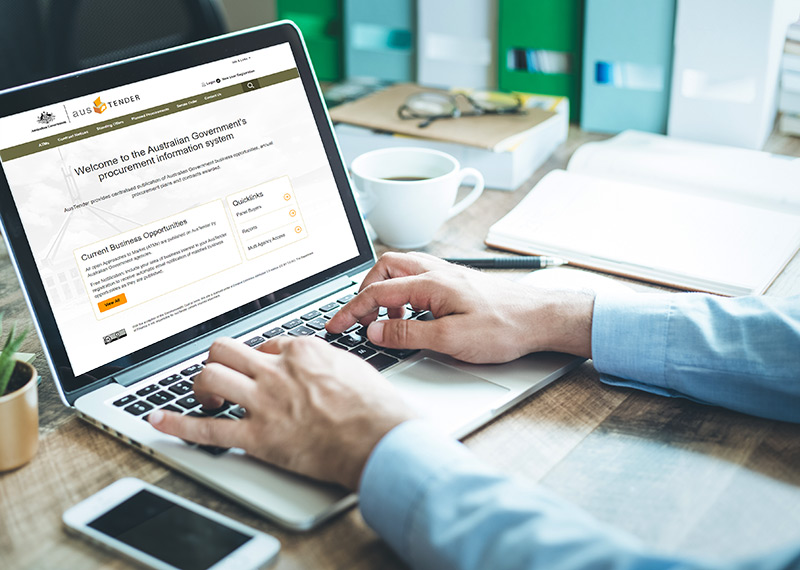
This information report seeks to provide greater transparency on procurement activity in the Australian public sector. This information report is neither an audit nor an assurance review and presents no conclusions or opinions. The report is presented in a variety of ways, including tables and figures, publicly available data from public sector procurement activity recorded in AusTender.
Entity
Across Entities
Contact
Please direct enquiries through our contact page.
Performance audit (Auditor-General Report No. 51 of 1999–2000)
Published: Thursday 29 June 2000
Published
The objective of the audit was to examine program management in the Training and Youth Division of the Department of Education, Training and Youth Affairs. In broad terms, the audit focused on the management frameworks at both Divisional and program level. Three of the Division's programs were selected for more detailed review as follows:
- Workplace English Language and Literacy;
- Literacy and Numeracy; and
- Support for New Apprentices.
Entity
Department of Education, Training and Youth Affairs
Performance audit (Auditor-General Report No. 22 of 2001–02)
Published: Tuesday 4 December 2001
Published
Personnel security, including the security clearance process, is a valuable and essential element of managing the risk inherent in allowing Commonwealth and other personnel access to sensitive information. This audit was designed to review security clearance and vetting policies and practices in a number of Commonwealth organisations and to consider if organisations were managing these processes effectively and efficiently and in accordance with Commonwealth policy, as outlined in the Protective Security Manual.
Entity
Across Agency
Performance audit (Auditor-General Report No. 4 of 1999–2000)
Published: Thursday 22 July 1999
Published
The audit reviewed fraud control arrangements in the Department of Employment, Education, Training and Youth Affairs. The objective of this audit was to establish whether the Department had developed a sound fraud control framework by examining the arrangements for: · policy and planning; · performance assessment; · quality assurance; and · training and awareness raising.
Entity
Department of Education, Training and Youth Affairs
Performance audit (Auditor-General Report No. 48 of 2001–02)
Published: Friday 10 May 2002
Published
The audit examined the administrative processes that the department has in place to support the administration of RAP. The objective of the audit was to determine whether funding was being allocated in accordance with the RAP policy guidelines and whether the department was managing RAP contracts to ensure that desired outcomes are achieved
Entity
Department of Transport and Regional Services
Performance audit (Auditor-General Report No. 40 of 2002–03)
Published: Tuesday 22 April 2003
Published
The audit assessed DITR's and the ATO's administration of the R&D Tax Concession including review processes for registration and subsequent expenditure claims, by eligible companies. In particular, the audit focussed on measuring performance, risk management, and information systems including security and data integrity.
Entity
Australian Taxation Office; Department of Industry Tourism and Resources
Performance audit (Auditor-General Report No. 5 of 2000–01)
Published: Wednesday 23 August 2000
Published
The ANAO undertook an audit of the framework and systems that Industry, Science and Resources had in place to prevent, control, monitor, detect and investigate fraud. The objective of the audit was to assess the effectiveness of these arrangements in relation to departmental administrative functions and program operations.
Entity
Department of Industry Science and Resources
Performance audit (Auditor-General Report No. 21 of 2001–02)
Published: Tuesday 20 November 2001
Published
The audit reviewed the policy advising functions of the Departments of Education, Training and Youth Affairs, Employment, Workplace Relations and Small Business, and Family and Community Services. The objective of the audit was to determine whether departmental quality management systems for policy advising were appropriate and the advice provided met expected standards for policy outputs.
Entity
Department of Education Training and Youth Affairs; Department of Employment Workplace Relations and Small Business; Department of Family and Community Services
Performance audit (Auditor-General Report No. 19 of 1998–99)
Published: Tuesday 8 December 1998
Published
The objective of the audit was to form an opinion on the administrative effectiveness and efficiency of DHAC's processes for planning the Commonwealth's Aged and Community Care program, in particular, on the questions of how well the planning process has contributed to realising the program objectives of achieving an equitable distribution of places between regions, and selecting suitable service providers.
Entity
Department of Health and Aged Care
Performance audit (Auditor-General Report No. 30 of 2000–01)
Published: Wednesday 7 March 2001
Published
The audit examined the efficiency and effectiveness of DEWRSBs administrative arrangements for the Work for the Dole Programme. The audit focused on the Community Work Coordinator tender assessment process, selection of projects, contract management arrangements and the mechanisms used for measuring the performance of the Programme against its objectives.
Entity
Department of Employment Workplace Relations and Small Business
Performance audit (Auditor-General Report No. 55 of 2002–03)
Published: Tuesday 24 June 2003
Published
The audit reviewed the Australian Taxation Office's fraud prevention and contol arrangements in relation to the Goods and Services Tax. The audit objective was to assess whether the ATO has implemented administratively effective GST fraud control arrangements, consistent with the Commonwealth Fraud Control Guidelines.
Entity
Australian Taxation Office
Performance audit (Auditor-General Report No. 37 of 1996–97)
Published: Wednesday 18 June 1997
Published
The objective of the audit was to provide assurance about the Australian Taxation Office's risk management approach and to add value to its administration by analysing the economy, efficiency, administrative effectiveness, equity and accountability of the related processes employed within the organisation. The ANAO reviewed the formal risk management process that the ATO uses to deal with all sources of risk for the organisation.
Entity
Australian Taxation Office
Performance audit (Auditor-General Report No. 44 of 1997–98)
Published: Wednesday 13 May 1998
Published
The Australian Diplomatic Communications Network was developed to provide a secure communication and automation capability for domestic offices and overseas posts. The audit focussed on project management of the ADCNET project, and in particular:
- how effectively the ADCNET project was managed;
- how effectively project risks were managed; and
- the extent to which project management processes have established whether ADCNET meets the specifications set by, and the expectations held by, DFAT, as well as any lessons to be learnt for this and other future projects.
Entity
Department of Foreign Affairs and Trade
Performance audit (Auditor-General Report No. 23 of 2002–03)
Published: Friday 20 December 2002
Published
Physical Security Arrangements in Commonwealth Agencies, No.23 2002-2003 Protective security involves the total concept of information, personnel, physical, information technology and telecommunications security. The Commonwealth's Protective Security policy is outlined in the Protective Security Manual (PSM). It provides specific guidance to agencies on the protection of the Commonwealth's assets, personnel and clients from potential security threats. This audit evaluated the protective security policies and practices of seven Commonwealth agencies to determine whether they had established an appropriate physical security control framework based on the principles outlined in Part E of the Commonwealth's Protective Security Manual. The ANAO also examined whether agencies had considered the risks of, and developed an appropriate policy statement on, the physical security arrangements for employees who work from home.
Entity
Across Agency
Performance audit (Auditor-General Report No. 22 of 2000–01)
Published: Thursday 14 December 2000
Published
The objective of this audit was to establish whether Defence has developed sound fraud control arrangements that are consistent with better practice and fulfil its responsibilities for the protection of public property, revenue, expenditure, and rights and privileges from fraudulent exploitation.
Entity
Department of Defence
Performance audit (Auditor-General Report No. 42 of 1998–99)
Published: Wednesday 26 May 1999
Published
The objective of the audit was to examine the effectiveness and efficiency of the administrative arrangements for the establishment and operation of the Green Corps program. Green Corps is a voluntary program for young Australians between 17 and 20 years old to receive accredited training in a range of skills such as bush regeneration and habitat protection. The program is delivered through a contractual arrangement. It was introduced in 1996 with a program allocation of $41.7 million over three years. The focus of the audit was on the Department of Education, Training and Youth Affair's administration of the program, including the management of the contract.
Entity
Department of Education, Training and Youth Affairs
Performance audit (Auditor-General Report No. 30 of 2002–03)
Published: Thursday 27 February 2003
Published
The Service Chiefs of Navy, Army and Air Force are accountable to the Chief of the Defence Force for the way that equipment is used by their Service. They are also accountable for the safety, fitness for service and environmental compliance of the equipment. The audit report deals with the way that the Service Chiefs are assured of the safety and suitability for service of the Australian Defence Force's (ADF's) ordnance systems. Ordnance systems include munitions such as missiles, shells and mines, and the auxiliary material necessary to aim, launch and guide munitions.
Entity
Department of Defence
Performance audit (Auditor-General Report No. 27 of 1999–2000)
Published: Thursday 27 January 2000
Published
The objective of this performance audit was to assess the effectiveness and consistency of risk management processes undertaken by the Australian Taxation Office in administering individual taxpayer refunds.
Entity
Australian Taxation Office
Performance audit (Auditor-General Report No. 7 of 1998–99)
Published: Monday 7 September 1998
Published
The objective of the audit was to determine the extent to which the new employment services market had been implemented effectively and efficiently in accordance with announced Government policy and timeframe.
Entity
Department of Education, Training and Youth Affairs
Performance audit (Auditor-General Report No. 44 of 2002–03)
Published: Friday 23 May 2003
Published
The objective of the audit was to determine whether the controls and measures employed by FaCS and Centrelink to deliver Parenting Payment Single (PPS) payments were effective and efficient. To achieve this, the audit focused on four key areas. These were:
- the quality of performance measures used by FaCS and Centrelink;
- the effectiveness of FaCS' methodology for estimating the levels of risk of incorrect payment to PPS customers and the impact of these incorrect payments on the integrity of program outlays;
- the correctness of Centrelink's processing of reassessments; and
- the improvements to preventive controls such as training, guidance material, and the Quality On-Line system.
Entity
Department of Family and Community Services; Centrelink
Performance audit (Auditor-General Report No. 9 of 2001–02)
Published: Thursday 16 August 2001
Published
The audit examined some key aspects of HRD in relation to Centrelink's Customer Service Officers (CSOs). The objective of the audit was to determine whether Centrelink had appropriate systems and strategies in place to ensure that its CSOs had access to the skills and knowledge necessary to meet expected levels of performance and customer service.
Entity
Centrelink
Performance audit (Auditor-General Report No. 12 of 1999–2000)
Published: Thursday 14 October 1999
Published
This audit examined the management of contracts for business support processes in eight Commonwealth organisations-six operating under the Financial Management and Accountability Act 1997, and two operating under the Commonwealth Authorities and Companies Act 1997. The objectives of this audit were to:
- provide assurance on the effectiveness of the management of contracted business support processes in selected organisations; and
- identify and disseminate better practices in related contract management.
Entity
Across Agency
Performance audit (Auditor-General Report No. 19 of 1997–98)
Published: Thursday 4 December 1997
Published
The objective of the audit was to report to Parliament on the economy, efficiency and administrative effectiveness of the risk management process in the Small Business Income business line. It follows Audit Report No.37 1996-97 and entitled Risk Management - Australian Taxation Office. That audit focused on broad strategic issues relevant to risk management in the Australian Taxation Office (ATO) as a whole. This audit follows the issues identified in that report into the day-to-day management of the Small Business Income as an example of how risk management operates in a significant element of the ATO.
Entity
Australian Taxation Office
Performance audit (Auditor-General Report No. 22 of 2002–03)
Published: Thursday 12 December 2002
Published
The audit theme was financial management and accountability. The audit concluded that six of the eight organisations had satisfactory payment of accounts processes and that GST administration control frameworks had been implemented. Payment of accounts processes could be improved by greater use of information technology whereas using risk management; formalising the BAS preparation procedures; and increasing monitoring and review procedures could improve GST administration.
Entity
Across Agency
Performance audit (Auditor-General Report No. 10 of 2001–02)
Published: Monday 17 September 2001
Published
The objectives of the audit were to determine whether agencies have implemented appropriate risk management strategies for the new banking arrangements, which came into operation on 1 July 1999 and whether cash funds are being managed in accordance with the appropriate legislation, the Commonwealth's agency banking guidance and generally accepted accounting practices. The scope of the audit was restricted to the departmental cash funds management and focused on risk management processes and management accounting controls adopted in the forecasting of cash flows, operation of bank accounts and placement of funds. The audit examined seven agencies, which are not named in the report.
Entity
Across Agency
Performance audit (Auditor-General Report No. 53 of 2001–02)
Published: Wednesday 29 May 2002
Published
The audit objective was to determine whether organisations had implemented adequate control frameworks and processes to mitigate the risks associated with GST obligations and transactions. The scope of the audit covered all aspects of GST processing relating to the revenue and expenditure accounting cycles in six Commonwealth organisations. Audit testing of transactions was based on a statistical sample of 160 GST transactions at each of the organisations.
Entity
Across Agency